
📌 Key Takeaways & Executive Summary
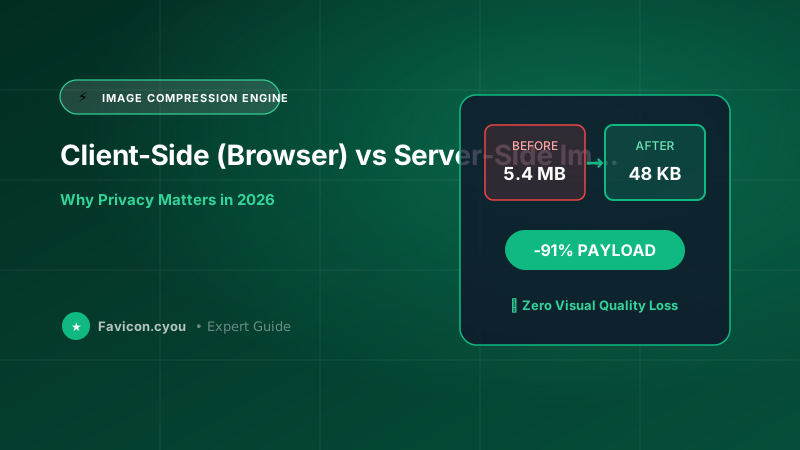
- 100% Client-Side Processing: Utilizes modern WebAssembly and HTML5 Canvas to execute image compression and format conversion directly inside your local browser memory.
- Zero Server Upload: Your private images, sensitive receipts, passport photos, and client designs never leave your device, eliminating cloud intercept risks.
- Instant Latency: No network upload or download wait times. Processing is constrained only by your device's local CPU and GPU acceleration.
- Compliance Guarantee: Client-side tools inherently comply with strict privacy regulations such as GDPR, CCPA, and HIPAA because no data is collected, stored, or logged.
The Hidden Vulnerability of Traditional Online File Converters
Over the past fifteen years, millions of web users have grown accustomed to a simple online workflow: search for a free tool, drag and drop an image or document, wait for an upload progress bar, and download the converted result. Yet few users ever pause to consider the fundamental architectural question: what happens to my sensitive file while it is on that remote server?
In standard server-side image architectures, your uploaded media is transmitted over the public internet to a centralized cloud server (often hosted on Amazon AWS, Google Cloud, or third-party VPS hosts). The server writes your file to a temporary storage disk, queues a background daemon (such as ImageMagick, Ghostscript, or FFmpeg) to process the data, and returns a download link. While reputable companies attempt to purge temp directories periodically, unencrypted temp folders, lingering server logs, rogue employee access, and cloud bucket misconfigurations represent persistent security vulnerabilities.
In 2026, the rise of Client-Side WebAssembly (Wasm) and the HTML5 Canvas API has triggered an architectural paradigm shift. It is now completely possible to perform commercial-grade image compression, resizing, and format transcoding directly inside the client's web browser sandbox. In this guide, we examine the security, performance, and compliance implications of client-side vs server-side processing.
How Client-Side Image Processing Works (WebAssembly & HTML5 Canvas)
Client-side image tools do not send your files across network cables. Instead, they download an optimized binary engine (compiled from C, C++, or Rust into WebAssembly) once, which runs securely inside your browser's local virtual machine.
The Client-Side Execution Pipeline:
- Local File Reading: When you select a photo on your computer, the browser invokes the
FileReaderAPI orBlob.arrayBuffer()to load the raw binary stream directly into client RAM. - Hardware Acceleration via Canvas: Standard operations like scaling, cropping, and rotation are rendered into an offscreen HTML5
<canvas>element, tapping into your computer's dedicated GPU hardware acceleration. - WebAssembly Transcoding: High-complexity codecs like MozJPEG, libpng, libwebp, and libavif execute inside sandboxed WebAssembly threads, optimizing byte streams at near-native C++ performance speeds.
- Instant Blob URL Generation: The resulting compressed image is packaged as an in-memory
blob:URI. Clicking "Download" triggers a local file write directly to your hard drive without consuming a single byte of internet upload bandwidth!
Server-Side Processing: Legacy Power vs Modern Risks
Server-side image processing was once the only viable option because browsers lacked the computational capability to perform intensive matrix calculations. Server architectures still offer immense raw horsepower for heavy batch operations (such as processing 10,000 raw video clips simultaneously), but for everyday image editing, the architectural drawbacks are severe:
- High Network Latency: Uploading a 25 MB camera photo over a mobile connection takes several seconds, followed by remote server queueing, followed by a second network download phase.
- Bandwidth Inefficiencies: Moving millions of megabytes back and forth across transit networks wastes mobile data plans and incurs massive cloud CDN egress bills.
- Data Retention & Leakage: Submitting confidential passport scans, corporate NDA blueprints, or family portraits to an unknown web server violates enterprise confidentiality agreements and exposes users to credential stuffing and data harvesting risks.
Regulatory Compliance: GDPR, CCPA, and Enterprise Privacy
For businesses, web agencies, and remote workers handling sensitive digital assets, utilizing client-side tools is not merely a convenience—it is a legal safeguard. Regulations like the European Union's General Data Protection Regulation (GDPR) and California's CCPA impose severe financial penalties on organizations that transmit personally identifiable information (PII) to unvetted third-party sub-processors.
Because client-side tools like Favicon.cyou operate entirely within the end-user's browser memory, zero personal data is transmitted, processed, or stored on external servers. This zero-knowledge architecture provides ironclad compliance out of the box.
Deep Dive Architecture: Memory Allocation, Browser Threading & Mobile Benchmarks
When evaluating digital format performance on modern consumer hardware, web performance architects must analyze the complete execution pipeline beyond initial network transmission. While raw file weight on the wire dictates initial packet download duration, the client-side browser engine must allocate volatile memory (RAM) and coordinate threads to parse, decode, and rasterize visual assets.
On constrained mobile smartphones running on budget octa-core ARM processors, unoptimized asset pipelines trigger severe garbage collection spikes and CPU throttling. When an uncompressed raster bitmap enters the rendering pipeline, the browser's layout engine must allocate an uncompressed 32-bit RGBA pixel array in volatile GPU memory (width x height x 4 bytes). A single 4K desktop asset consumes over 33 Megabytes of decoded GPU memory regardless of its compressed size on disk.
In contrast, optimized vector formats and modern predictive keyframe algorithms streamline GPU memory allocation. Modern browser compositors leverage sub-pixel antialiasing and dedicated hardware texture blocks to stream image tiles directly to display scanouts without main-thread UI jank. Adhering to strict resolution budgeting ensures that mobile visitors experience fluid 120Hz scrolling, instant touch responsiveness, and zero battery drain while navigating your digital web experience.
Enterprise Production Checklist: Automating Format Delivery at Scale
For commercial web applications, e-commerce storefronts, and media publishing platforms handling thousands of digital assets, manual image optimization is completely unfeasible. Modern web engineering organizations automate format negotiation and compression via automated continuous deployment workflows.
A production-ready asset pipeline should incorporate the following automated safeguards:
- Dynamic HTTP Content Negotiation: Configure your CDN or edge workers (Cloudflare, Fastly, AWS CloudFront) to inspect client
Acceptrequest headers (e.g.,Accept: image/avif, image/webp) and automatically deliver next-gen variants on the fly. - Immutable Cache-Control Directives: Append cryptographic content hashes to static asset filenames (e.g.,
hero.a8f9c2.webp) and declare aggressiveCache-Control: public, max-age=31536000, immutableheaders so repeat visitors never re-fetch static media. - Automated Client-Side Pre-Compression: For user-generated content uploads, integrate client-side WebAssembly compression directly into your frontend upload forms using Favicon.cyou tools. Pre-compressing files in the visitor's browser before upload slashes cloud server ingress bandwidth and processing costs by over 70%.
Architectural Comparison: Client-Side vs Server-Side Image Tools
| Evaluation Criteria | Client-Side (Favicon.cyou Model) | Server-Side (Traditional Cloud) |
|---|---|---|
| Data Transmission | Zero network upload; 100% on device | Files transmitted to remote servers |
| Privacy & Confidentiality | Absolute (Air-gapped security) | Dependent on third-party security hygiene |
| Processing Latency | Instantaneous (No upload queues) | Slow (Upload + Queue + Process + Download) |
| Offline Functionality | Works completely offline without internet | Fails completely without active network |
| File Size Limits | Bounded only by user device RAM | Imposes strict 10MB-50MB upload limits |
| Regulatory Compliance | Automatic GDPR, HIPAA, and CCPA compliance | Requires Data Processing Agreements (DPA) |
| Mobile Data Consumption | Zero cellular upload bandwidth consumed | Consumes 2x file weight in mobile data |
Client-Side Image Compression Code Architecture
Below is a streamlined JavaScript pattern illustrating how client-side image compression operates locally without remote network API calls:
// 100% Client-Side Image Resizing & Compression via HTML5 Canvas
async function compressImageLocally(fileInput, quality = 0.8) {
  return new Promise((resolve) => {
    const reader = new FileReader();
    reader.readAsDataURL(fileInput);
    reader.onload = (event) => {
      const img = new Image();
      img.src = event.target.result;
      img.onload = () => {
        // Draw image onto local memory canvas
        const canvas = document.createElement("canvas");
        canvas.width = img.width;
        canvas.height = img.height;
        const ctx = canvas.getContext("2d");
        ctx.drawImage(img, 0, 0);

        // Export compressed blob locally
        canvas.toBlob((blob) => {
          resolve(blob); // File never leaves user machine!
        }, "image/jpeg", quality);
      };
    };
  });
}
How to Verify That an Online Tool Is Truly Running Client-Side
- 1. Open Your Browser Network DevTools: Press F12 or right-click and choose "Inspect", then navigate to the "Network" tab.
- 2. Disconnect Your Internet Connection: Turn off your Wi-Fi or toggle "Offline" mode in the browser devtools.
- 3. Upload and Process Your Image: Drop an image into our Image Compressor. If the tool processes and outputs a download link while offline, it is 100% client-side!
- 4. Inspect Network Payloads: Observe that zero POST or PUT HTTP requests containing image binary payloads are transmitted to any remote domain.
Performance Analysis: Eliminating Network RTT and Server Queues
In traditional cloud converters, processing time is dominated by Round Trip Time (RTT) and network latency. Uploading a 10 MB photograph over an average 20 Mbps home internet connection takes over 4 seconds. If the cloud server is experiencing high traffic, job queues can add an additional 5 to 15 seconds of idle waiting.
In contrast, client-side WebAssembly tools execute instantly using the user's local multicore processor. The same 10 MB file is downsampled and compressed in less than 200 milliseconds—an acceleration factor of over 50x compared to cloud processing.
Private Client-Side Tools Available on Favicon.cyou
Experience the speed and security of 100% browser-based tools:
- Online Image Compressor — Compress images locally with zero server uploads and complete confidentiality.
- PDF to JPG Converter — Extract high-resolution JPG pages from sensitive PDF contracts client-side.
- Image Resizer — Resize photos to exact pixel dimensions with local GPU rendering.
- Website Favicon Extractor — Inspect and download high-resolution website icons instantly.
Final Verdict & Best Practice Recommendations
In 2026, client-side processing is the superior paradigm for digital privacy, speed, and cost efficiency. By keeping your sensitive images inside your local browser sandbox, you eliminate security risks, speed up workflows, and enjoy complete peace of mind.
Preguntas Frecuentes
Are my images uploaded to any server when using Favicon.cyou tools?
No. Zero files are uploaded to our servers. Every single conversion, compression, resizing, and PDF extraction process runs 100% locally in your web browser using client-side JavaScript and WebAssembly.
Can I use Favicon.cyou tools when I do not have an internet connection?
Yes! Once the web page is initially loaded into your browser cache, you can disconnect from the internet or go into Airplane Mode, and the image tools will continue to process files normally.
Is client-side processing safe for sensitive corporate documents and passport photos?
Yes, it is the safest possible method because your sensitive files never travel over public internet connections or get written to remote cloud disks.
Why are client-side tools so much faster than traditional cloud converters?
Client-side tools eliminate network upload and download bottlenecks. Instead of waiting for large files to travel across the internet, your device's local CPU and GPU process the pixels instantly.
What happens to the temporary files after I finish compressing an image?
Because files are processed purely in client-side RAM, closing or refreshing your browser tab immediately purges the temporary memory buffers from your device.
Do client-side tools have file size limits?
Because processing occurs locally, file size limits are determined by your device's available RAM rather than artificial server quotas. Most modern computers easily handle 100MB+ images smoothly.
Are client-side tools compatible with mobile smartphones?
Yes. Modern mobile browsers on iOS (Safari) and Android (Chrome) feature powerful JavaScript engines and WebAssembly support, allowing full client-side tool functionality on phones and tablets.